
Enterprise data recovery
Enterprise Data Recovery
Turn “we have backups” into an executable, timed and reviewable recovery path across recovery objects, dependency order, isolated environments and business validation.
Recovery objects
Objects and recovery order
A business service often depends on virtual machines, databases, files, configuration, identities, certificates and external interfaces. “Restore the server” can still leave critical dependencies missing.
Create a business-priority recovery register with copy location, recovery point, owner and validation method for every object.
- Business priorityOrder recovery by criticality, outage impact and dependencies.
- Recovery pointConfirm acceptable data points, log ranges and consistency needs.
- Recovery ownershipAssign technical execution, business approval and escalation ownership.
Isolated recovery workspace
Isolate first, then return to production
The recovery environment needs compute, storage, networking, identity and security while keeping unvalidated systems away from production. Capacity gaps, address conflicts and missing access all extend recovery time.
Prepare network zones, temporary addressing, validation accounts, malware checks and data destinations so recovery can be repeated.
Isolated recovery workspace
- Technical validationData state and integrity evidence
- Business confirmationUsable business scenario evidence
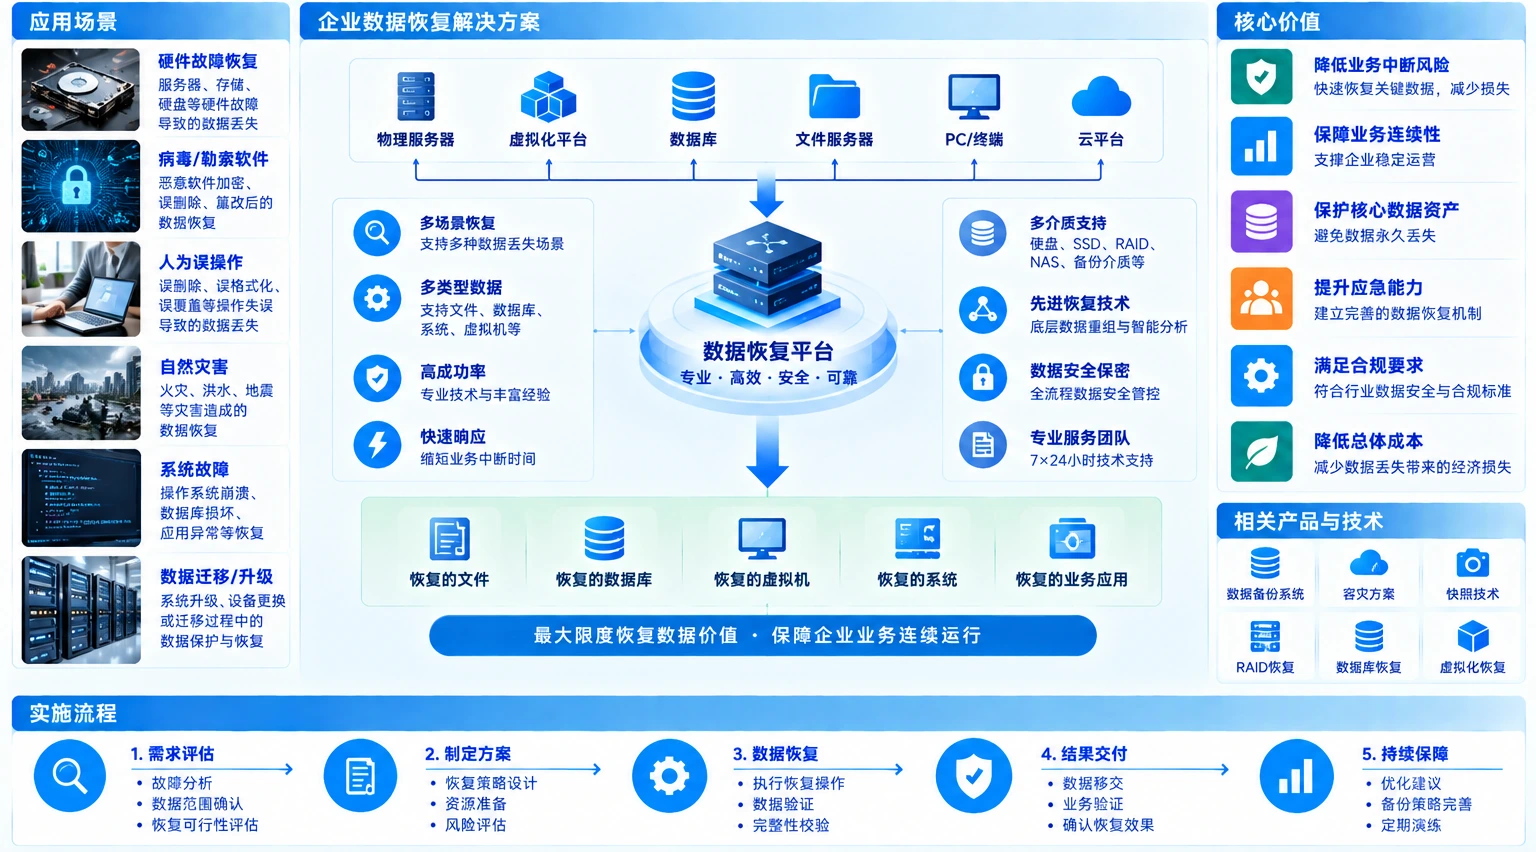
03 / Data and business validation
Validate data and business use
A booted system, visible files or an online database do not mean the business has recovered. Validate data points, record counts, application access, key transactions, interfaces and reports.
Technical validation
Timestamp, counts, checksums, logs and consistency are checked against the recovery target.
Business confirmation
Login, permissions, interfaces, transactions and reports are confirmed by the business owner.
Technical teams confirm platform state while business owners approve critical scenarios; both determine whether to proceed or roll back. Record technical results, business conclusions, open issues and decisions.
04 / Exercises and operations
A repeatable recovery runbook
Recovery capability drifts as versions, capacity, networks and teams change. Regular exercises update scripts, contacts, timing, failback conditions and resource headroom.
Every exercise records planned-versus-actual differences and carries issues into remediation and retesting.
- RunbookRecord prerequisites, steps, commands, checkpoints and stop conditions.
- Timing and gapsCompare actual RPO/RTO with targets and locate waits and bottlenecks.
- Failback and retestDefine production failback, data resynchronization and the next exercise.
Next step
Make the recovery path reviewable.
Bring the current copies, dependencies, recovery targets or exercise record.
Discuss recovery scope