
Network equipment selection · boundary security delivery
Next-generation firewall deployment
For enterprise internet exits, branches, data centres and remote VPN, scope next-generation firewall selection and pricing against your topology, traffic and licences, then plan policy review, phased migration, testing and handover.
Choose the right equipment and deployment model.
Start product selection by checking form factor, interfaces and management, then confirm the model against the existing network, traffic, policy scope and expansion plan.
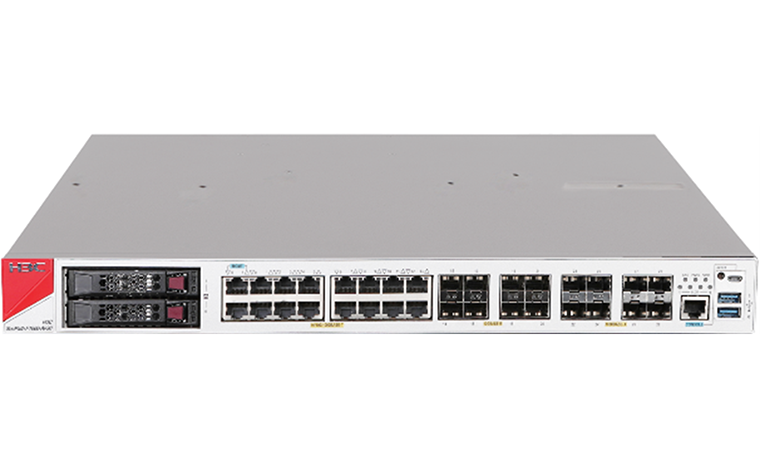
Deployment model
Desktop, rack or virtual form factors can match branches, exits, data centres or cloud environments.
Interfaces and high availability
Check uplink types, zone count, bypass conditions, HA relationships and existing links.
Licensing, subscriptions and maintenance
Confirm policy management, security features, log retention, remote access, licence and subscription terms, and maintenance responsibilities.
Define the equipment, interfaces, business traffic, security features and subscriptions before agreeing whether policy migration, testing, handover and maintenance are included. Confirm the final model and capabilities against formal product documentation and technical review. For related hardware supply, review the enterprise IT procurement catalogue; availability, licences and prices require project confirmation.
Deployment position and key capabilities
Policy needs a clear boundary.
Office internet, branch interconnection, data centres, cloud resources and remote work may use different paths. Map exits, zones, applications and identities before deciding form factor, interfaces, redundancy and policy scope.
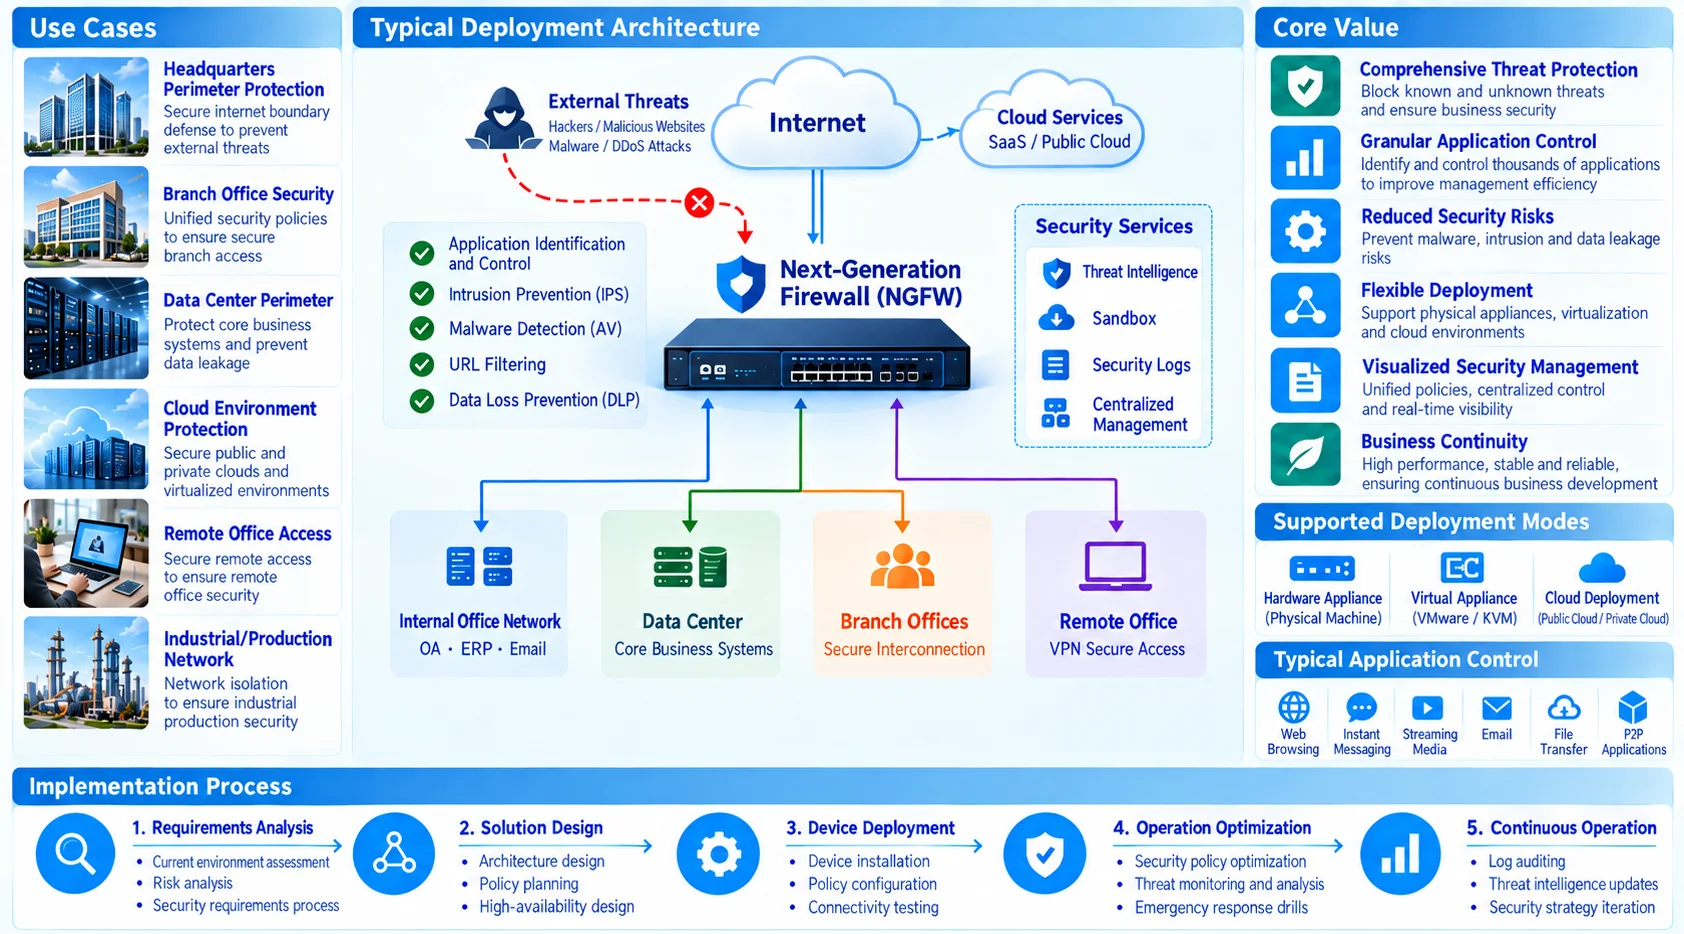
Rules, NAT and VPN
Design them together with logging.
- Application / identity recognition and access policy
- Distinguish business, identity, zone, time and exception conditions.
- NAT, VPN and boundary controls
- Confirm paths for public services, branch interconnection and remote access.
- Threat protection and audit logging
- Set inspection scope by business need so matches and changes remain reviewable.
Implementation and migration,
start with the rule baseline.
Before implementation, organise existing rules, objects, NAT, VPN and business paths. During cutover, reduce impact with observation, pilots, phased switching and rollback windows.
- Inventory
Organise the existing topology, rules, objects, logs and dependencies.
- Observe
Identify real business traffic, exceptions and undocumented paths.
- Cut over
Migrate in phases using pilots, windows and rollback conditions.
- Review
Validate access, threat policy, logs and business confirmation.
Operations and handover,
make future changes evidence-based.
Every rule should state its purpose, owner and next change method. During later adjustments, operations can find the impact first, then decide whether to allow, tighten or roll back.
View network and information security servicesHow can a firewall remain maintainable after delivery?
Keep objects, rule purposes, match results, configuration backups, change records and review methods so later adjustments have evidence.
- Object naming and rule descriptions
- Policy matches and audit logging
- Configuration backups and change records