
Application declarations
Images / Replicas / Resource requests
Submitted by kubectl or delivery tools
Virtualization and cloud platforms / Container orchestration
Let the cluster continually reconcile the state applications need. Make container deployment, service access and resource allocation repeatable instead of maintaining servers one login at a time.
Understand application operation before deciding how much platform to build.
Understanding Kubernetes
Kubernetes is an open-source orchestration system for containerized applications. Define images, replicas and resource requirements; the cluster schedules workloads and checks actual state. It does not replace application development or automatically solve every business failure.
Frequent releases, inconsistent environments and teams competing for servers make shared deployment/resource rules valuable. Environments with few, infrequently changing applications should compare existing virtualization with container-platform management costs first.
Cluster architecture
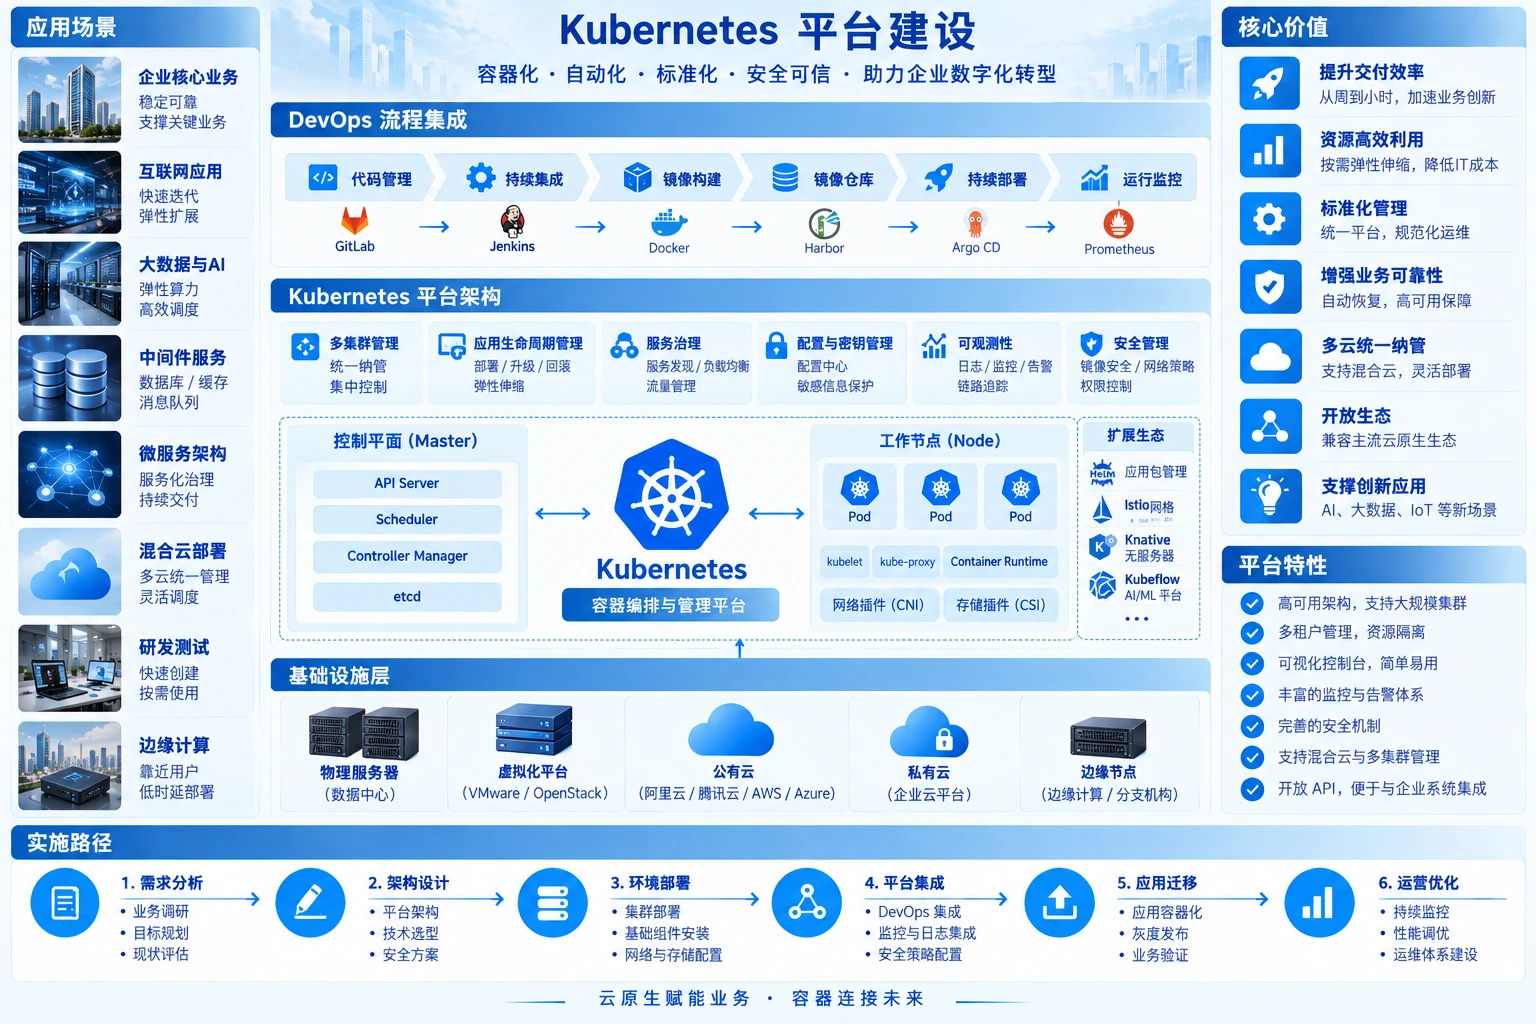
The control plane coordinates; worker nodes run applications. Users reach Pods through application service entry points, not through the API Server as a business-traffic proxy. The diagram distinguishes these paths.
Images / Replicas / Resource requests
Submitted by kubectl or delivery tools
Runtime dependencies A registry supplies images; CNI networking connects Pods; storage provides persistent volumes where needed. Ingress controllers, storage plugins and network-policy support require separate selection and configuration.
Relationships are illustrative, not physical component counts or production traffic. Availability, recovery speed and data protection depend on deployment and application design; animation is not live monitoring.
From image to runtime
Pin runtime environments and versions, separating images, configuration and business data. Validate startup, health checks and shutdown behavior.
Use registry versions and permissions. Integrate build, scanning and signing capabilities with the existing toolchain as needed.
Configure readiness checks, rollout pace and resource headroom. Verify real business functions during deployment, not just container startup.
Observe logs, metrics and alerts. Application rollback also requires checking whether database and configuration changes are reversible.
Keeping the platform operational
Plan ingress, discovery, address ranges and access boundaries. Separate production, testing and teams with explicit permissions and network rules, not namespace names alone.
Distinguish stateless and stateful workloads; check storage performance, mount modes, backups and recovery. Remounting a volume is not an independent backup.
Establish metrics, logs, alert owners and maintenance windows. Include node maintenance, certificate expiry and cluster upgrades in daily procedures so the platform remains usable beyond deployment day.
Where to start
Provide repeatable project environments with quotas and expiry/reclamation rules. The goal is repeatability, not unlimited provisioning.
Connect releases, service access and operating visibility. Migrate microservices gradually without requiring every legacy system to change at once.
Coordinate with Hybrid Cloud to assess placement. Containerized AI tasks also require GPU drivers, device integration and scheduling; adding cards alone is not enough.
Frequently asked questions
VMs provide relatively independent OS environments. Kubernetes deploys and operates containerized workloads. Cluster nodes can be physical servers or VMs; the technologies can work together rather than necessarily replace one another.
No. Assess OS, dependencies, state/storage, licenses, external interfaces and operating model. Start with a pilot having clear dependencies; retain or separately adapt systems that cannot be containerized directly.
No. Integrate code management, builds, registries, delivery, logs, alerts and permissions with the existing toolchain. GitLab, Harbor and Argo CD in the diagram are optional examples, not default components in every cluster.
No. Recreating Pods or restarting containers does not recover lost business data or eliminate dependency failures. Design replicas, availability zones/failure domains, backups, recovery exercises and application-level tolerance.
Yuqi Intelligent plans clusters, configures nodes/network/storage, deploys container platforms, integrates release tools and trains operations around existing applications and team workflows. Pilot one application, then expand from validated results.
Next step / Technical discussion
Share runtime environments, release frequency, dependencies and management challenges to define pilot scope and implementation order.